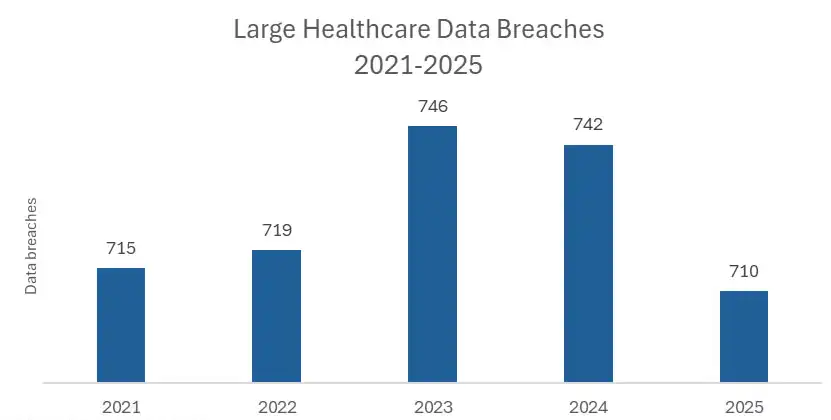
Healthcare data breaches now cost more to resolve than in any other industry, and regulators have not slowed down. According to HIPAA Journal’s 2025 Healthcare Data Breach Report, 710 healthcare data breaches affecting 500 or more individuals were reported to the U.S. Department of Health and Human Services (HHS) Office for Civil Rights (OCR).
For CIOs, CTOs, and enterprise architects building or maintaining systems that touch patient data, a HIPAA compliance checklist is no longer a compliance department’s problem. It is a product, security, and business continuity requirement that shapes architecture decisions.
A healthcare application can be feature-rich and still expose an organization to compliance risk if privacy, security, vendor, and operational controls are not designed together.
This guide brings together the Privacy Rule, Security Rule, Breach Notification Rule, Omnibus Rule, and Enforcement Rule into a single, practical HIPAA compliance requirements checklist built for decision-makers.
The blog also covers administrative, physical, and technical safeguards, along with requirements specific to healthcare software and apps. It highlights common compliance gaps and explains what your organization needs to document for an OCR audit.
Key Takeaways
|
What Is HIPAA Compliance and Who Must Meet HIPAA Requirements
HIPAA compliance means adhering to the Health Insurance Portability and Accountability Act, the U.S. federal law that sets national standards for protecting patient health information. It applies primarily to organizations operating in the United States, but it also reaches foreign vendors that process data on behalf of U.S. healthcare organizations.
Meeting HIPAA requirements is not optional once an organization creates, receives, stores, or transmits patient data in any identifiable form, whether that data lives in an EHR, a mobile app, or a third-party analytics platform.
Who must comply with HIPAA Privacy Standards?
HIPAA obligations fall on two groups. Covered entities and business associates together form the full compliance perimeter, and the Omnibus Rule made both directly liable for violations.
- Covered Entities: Hospitals, clinics, health plans, pharmacies, and healthcare clearinghouses that directly provide or pay for care.
- Business Associates: Vendors, contractors, and technology partners, such as cloud hosts, billing firms, and healthcare software development companies, that handle PHI on a covered entity’s behalf.
- Subcontractors: Any vendor working downstream of a business associate that also touches PHI inherits the same obligations.
What Data HIPAA Protects?
Protected Health Information (PHI) covers any individually identifiable health information, including names, dates, diagnoses, and billing records, in any format. When that information is created, stored, or transmitted digitally, it becomes Electronic Protected Health Information (ePHI), the category most enterprise architecture decisions revolve around. HIPAA recognizes 18 specific identifiers; even one alongside health data is enough to classify it as PHI.
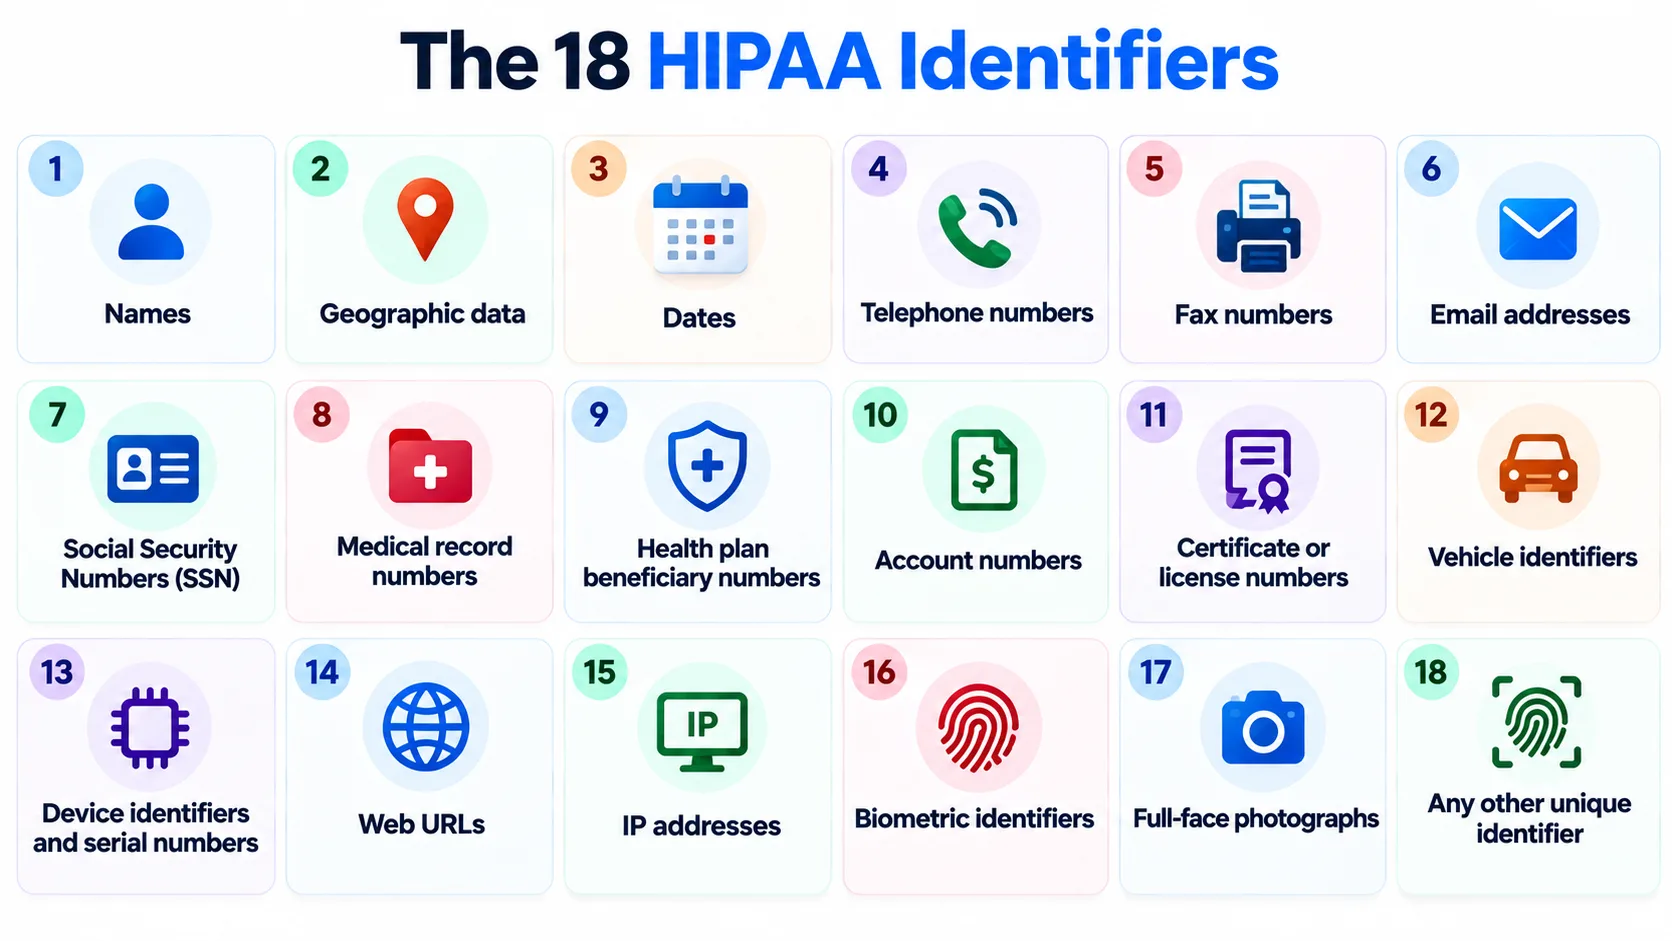
The Department of Health and Human Services (HHS) lists the 18 HIPAA identifiers as follows:
- Names: Full names or initials.
- Geographic data: All geographic subdivisions smaller than a state (such as street address, city, county, precinct, and ZIP code)
- Dates: All elements of dates related to an individual (except the year), including birth date, admission date, discharge date, date of death, and exact ages over 89.
- Telephone numbers: Home, work, or mobile numbers.
- Fax numbers: Personal or business fax contacts.
- Email addresses: Electronic mail contacts.
- Social Security Numbers (SSN): Individual national identification numbers.
- Medical record numbers: Patient hospital or clinic identification files.
- Health plan beneficiary numbers: Insurance and policy ID numbers.
- Account numbers: Patient financial or billing numbers.
- Certificate or license numbers: Professional or driver licenses.
- Vehicle identifiers: Serial numbers and license plate numbers.
- Device identifiers and serial numbers: Hardware or equipment tracking codes.
- Web URLs: Specific website links or addresses.
- IP addresses: Internet Protocol computer network addresses.
- Biometric identifiers: Fingerprints, voiceprints, or retinal scans.
- Full-face photographs: Comparable or detailed facial images.
- Any other unique identifier: Any distinct identifying characteristic, code, or number assigned to the individual
What HIPAA Compliance Rules Does Your Organization Need to Follow?
HIPAA rules break down into five components. Each governs a distinct part of how patient data must be handled, secured, and reported on.
| Rule | What It Governs | Primary Owner |
| HIPAA Privacy Rule | Who may access, use, and disclose PHI, and patients’ rights over their own records. | Privacy Officer |
| HIPAA Security Rule | Administrative, physical, and technical safeguards for ePHI. | Security Officer |
| Breach Notification Rule | Timelines and procedures for reporting a breach to individuals, HHS, and media. | Compliance / Legal |
| Omnibus Rule | Extends direct liability to business associates and subcontractors. | Legal / Procurement |
| Enforcement Rule | OCR investigation procedures and civil monetary penalty structure. | Executive Leadership |
The Privacy Rule
The HIPAA Privacy Rule governs how covered entities may use and disclose PHI and establishes rights for individuals. Technology teams should support minimum-necessary access, appropriate authorization workflows, data access requests, correction processes, and privacy notices where applicable.
The Security Rule
The HIPAA Security Rule is the operational core of technical compliance. It requires administrative, physical, and technical safeguards for every system that creates, stores, or transmits ePHI. It applies whether that system is a legacy on-premises database or a cloud-native SaaS product.
The Breach Notification Rule
Under the Breach Notification Rule, covered entities must notify affected individuals within 60 days of discovering a breach. Breaches affecting 500 or more individuals require immediate notification to HHS.
In many cases, local media can report smaller breaches annually. OCR enforcement activity around this rule has intensified as ransomware and vendor breaches have grown more common.
The Omnibus Rule
The Omnibus Rule closed a longstanding gap. It made business associates and subcontractors directly accountable under HIPAA rather than only contractually accountable to a covered entity. Every BAA in force today reflects this rule.
The Enforcement Rule
The Enforcement Rule gives OCR authority to investigate complaints, conduct audits, and assess civil monetary penalties. It is the mechanism that turns the other four rules from policy into financial and legal exposure.
The Complete HIPAA Compliance Checklist for Healthcare Organizations
This is the working HIPAA Compliance Checklist most audits are measured against. Administrative, Physical, and Technical Safeguards are all mandatory under the Security Rule, and an organization strong in one category cannot compensate for weakness in another.
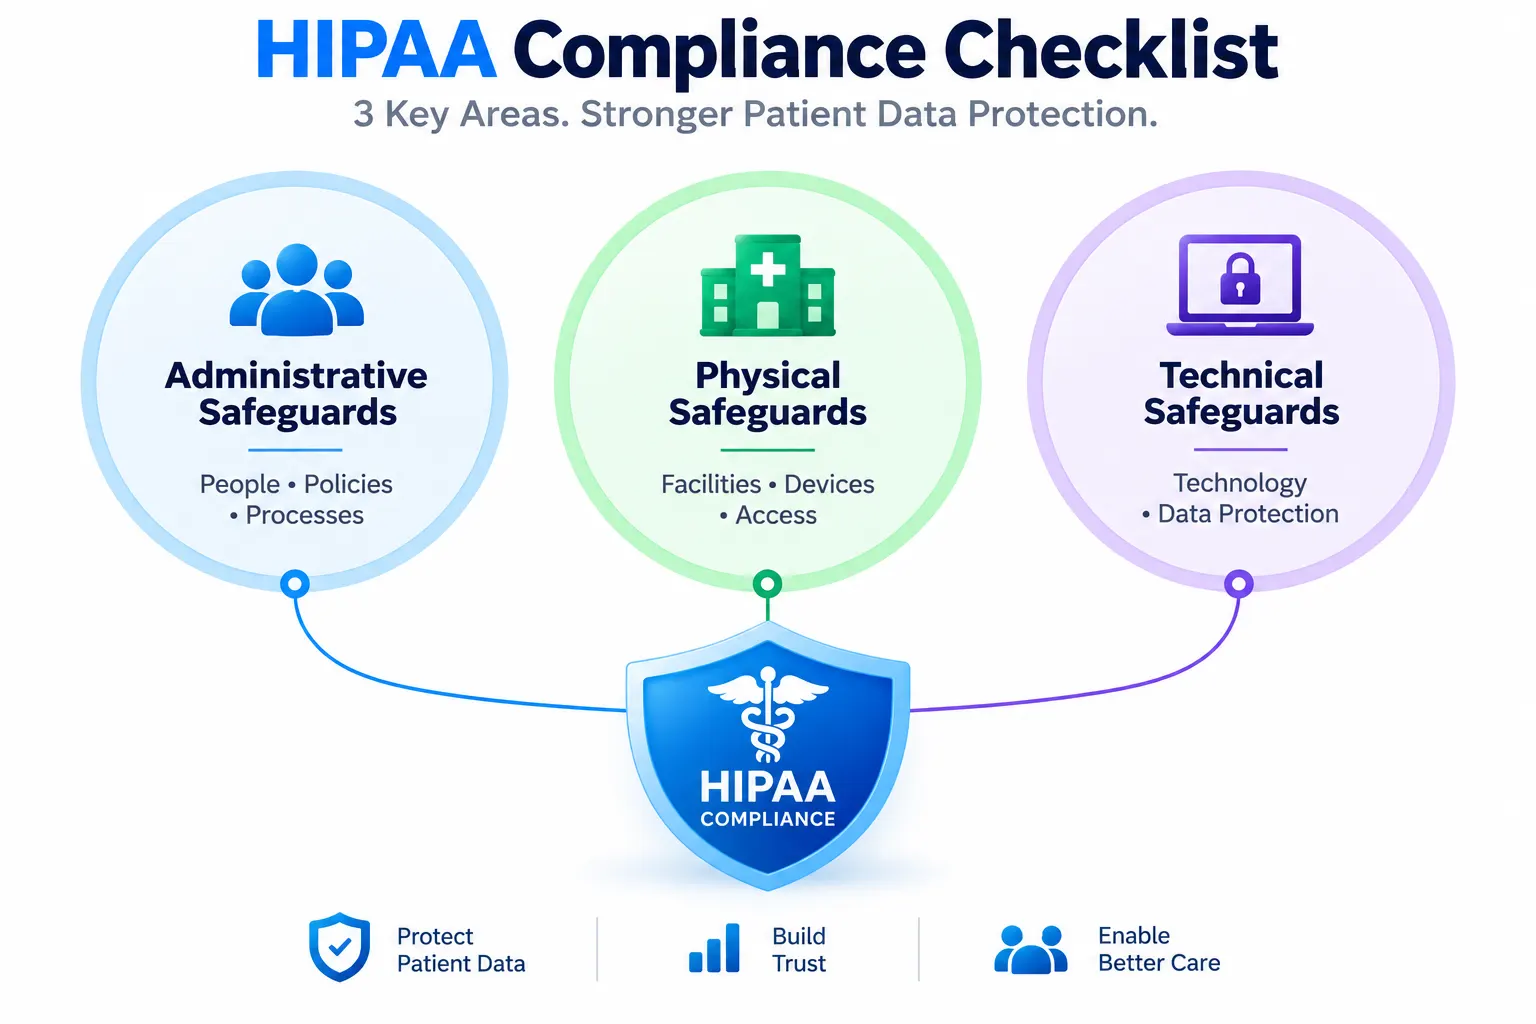
Administrative Safeguards
- Designate a HIPAA Privacy Officer and Security Officer, or a combined Compliance Officer for smaller organizations.
- Conduct a formal security risk assessment at least annually and after any significant system or vendor change.
- Provide documented workforce training on PHI handling to every employee with system access, during onboarding and after any policy change.
- Implement a sanctions policy for employees who violate PHI handling procedures.
- Maintain an incident response plan that defines detection, escalation, and reporting steps.
Physical Safeguards
- Restrict facility access to authorized personnel using key cards, badges, or equivalent controls.
- Secure workstations and devices, including remote and personal devices used to access ePHI, with screen locks and encryption.
- Establish disposal procedures for hardware, drives, and media that once stored ePHI.
Technical Safeguards
This HIPAA security rule checklist covers the controls that engineering and platform teams own directly:
- Encrypt ePHI at rest and in transit; encryption is the single most cited control in OCR settlement agreements.
- Implement role-based access control that enforces the minimum necessary standard at the field level, not just the page level.
- Assign unique user identification to every account; shared logins break audit traceability.
- Enable audit controls that log every access to and modification of a patient record, including who, when, and what changed.
- Enforce automatic session logout after inactivity, and document emergency access procedures for urgent care scenarios.
- Apply integrity controls, such as checksums, to prevent undetected alteration of ePHI.
HIPAA Compliance Requirements Checklist for Healthcare Apps and Software
HIPAA compliance for healthcare apps rests on infrastructure, not interface. A polished front end does nothing for compliance if the backend storing patient records lacks encryption, access controls, and audit logging. Meeting HIPAA compliant app development requirements involves organizational safeguards that must work independently and effectively.
Foundational Technical Controls for Compliant Systems
- Encryption of ePHI at rest and in transit, enforced at the infrastructure level, not bolted on afterward.
- Field-level, role-based access controls that reflect the minimum necessary standard, not just page-level permissions.
- Tamper-resistant audit logs retained for at least six years, capturing every record access and change.
- Two-factor authentication and strong password policies on every account with PHI access.
- Documented data backup and disaster recovery procedures to preserve patient record availability.
- A signed BAA with every vendor in the data path, including scheduling tools, analytics platforms, and AI features.
Where Compliance Gaps Most Commonly Appear
Understanding the requirements is the easy part. In practice, gaps tend to cluster in four predictable places:
- The prototype-to-production gap: Teams build and test on non-compliant infrastructure, then real patient data enters the system before migration to a compliant backend is complete.
- The vendor chain gap: A primary platform is compliant, but a scheduling tool, payment processor, or AI feature further down the stack was never evaluated for its own BAA and safeguards.
- The access-control depth gap: Role-based access exists at the page level but fails at the field level, so a billing employee can still see clinical notes.
- The logging gap: Standard application logs capture errors and system events, but not the record-level, user-attributed access history HIPAA’s audit control requirement demands.
Checklist for HIPAA Compliance Across Patient-Facing Systems
The same core requirements apply differently depending on what the system does. Building HIPAA compliant healthcare apps means adapting the checklist to the specific data flows of each system type.
- Patient intake forms: Collect PHI from the first field submitted, so the backend needs a signed BAA, encryption, and logged access from day one. General-purpose form tools rarely meet this bar out of the box.
- Patient portals: Involve patient-facing access to their own records, requiring strong authentication, session management, and permissions scoped strictly to each patient’s own data.
- Referral tracking systems: Move PHI between providers, so encryption and access controls apply to data in transit at every handoff, not only to data at rest.
- Care coordination and CRM tools: Involve ongoing, multi-role access to PHI, making field-level permissions and complete view-and-edit logging essential, not optional.
HIPAA Compliance Checklist for Startups and Small Businesses
A HIPAA compliance checklist for startups looks different from an enterprise rollout, but the underlying requirements do not shrink. HIPAA compliance for small businesses still requires all three safeguard categories; what changes is sequencing and budget.
- Build on infrastructure that includes a signed BAA and technical safeguards by default, rather than retrofitting compliance later. Industry estimates put retrofit costs at 100 to 200 percent of the original build.
- Assign compliance ownership early, even if a single founder wears the Privacy and Security Officer hats.
- Document the risk assessment and policies before the first real patient record enters the system, not after.
- Vet every third-party integration, including analytics and AI tools, for its own BAA before connecting it to patient data.
How to Conduct a Security Risk Assessment
A security risk assessment is not a formality. It establishes what could go wrong, how likely and consequential those events may be, and which safeguards are appropriate. HHS guidance describes risk analysis as foundational to implementing Security Rule safeguards.
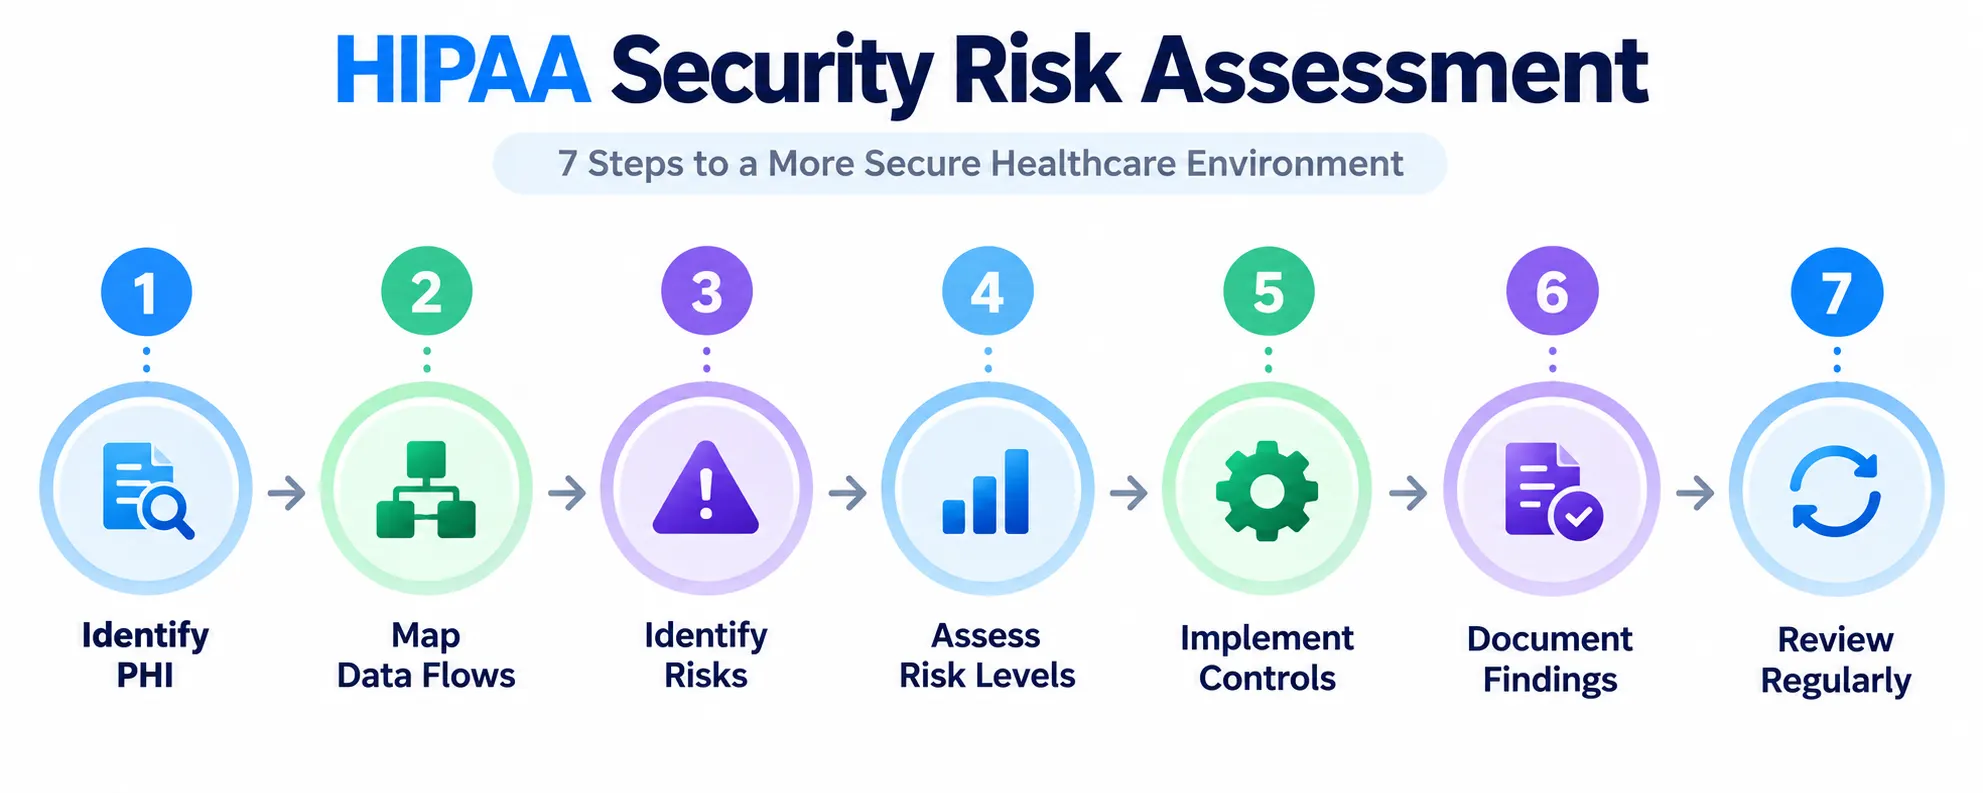
- Inventory assets and data stores that handle ePHI.
- Map data flows and trust boundaries.
- Identify threats and vulnerabilities, including third-party and operational dependencies.
- Estimate likelihood and potential impact.
- Select and prioritize safeguards.
- Document residual risk, owners, remediation dates, and accepted exceptions.
- Reassess when major architectural, organizational, or threat changes occur.
How to Become HIPAA Compliant Step by Step
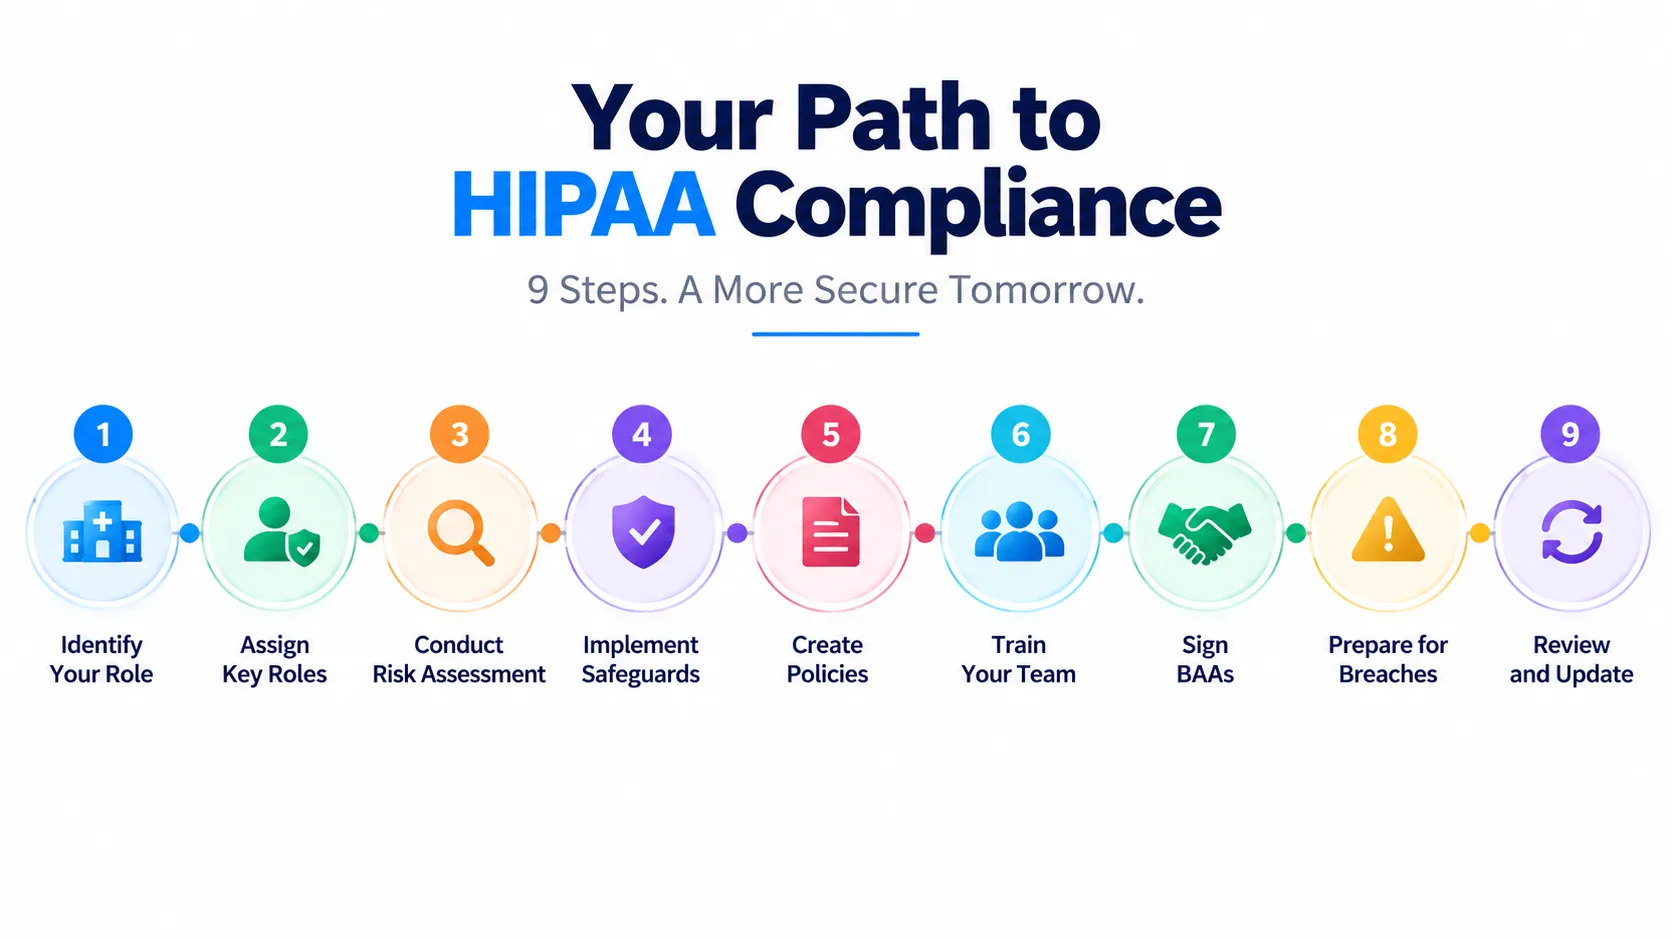
Organizations asking how to become HIPAA compliant can follow this sequence:
- Determine whether your organization is a covered entity, a business associate, or both.
- Assign a Privacy Officer and a Security Officer, or a combined role for smaller teams.
- Conduct a comprehensive risk assessment across every system that touches PHI.
- Implement administrative, physical, and technical safeguards based on the assessment’s findings.
- Draft and distribute written policies, procedures, and a Notice of Privacy Practices.
- Train the entire workforce and document completion.
- Secure signed BAAs with every vendor touching PHI.
- Establish breach detection and notification procedures aligned to the 60-day requirement.
- Review, update, and re-document the program on an ongoing basis, not as a one-time project.
Application Security and DevSecOps Best Practices for HIPAA Compliance
For engineering organizations, compliance should become part of the software delivery lifecycle. Treat security requirements as architecture and engineering requirements, then verify them through automated and manual testing.
- Define PHI boundaries during architecture and threat modeling.
- Apply least privilege to application roles, service accounts, APIs, and administrative tooling.
- Protect secrets and credentials through centralized secrets management.
- Use secure coding practices and dependency management.
- Scan code, containers, infrastructure, and dependencies as appropriate.
- Test authentication, authorization, input validation, session management, logging, and API security.
- Separate development, test, and production environments and control production data use.
- Document security testing, findings, remediation, and release approvals.
How to Manage PHI Throughout Its Lifecycle
Compliance risk often emerges at the edges of the primary application: exports, logs, backups, support tools, analytics pipelines, and integrations. A defensible architecture treats PHI as a lifecycle, not a database record.
- Collect only the data needed for the defined purpose.
- Classify PHI and ePHI consistently across repositories and services.
- Apply role-based and, where appropriate, attribute-based access controls.
- Review privileged access and remove stale accounts promptly.
- Protect backups and test recovery procedures.
- Define retention, archival, deletion, and disposal processes consistent with applicable obligations.
- Prevent PHI from leaking into application logs, debugging tools, analytics platforms, or unmanaged endpoints.
A Practical HIPAA Compliance Audit Checklist
| Area | Evidence to verify | Status |
| Governance | Named owners, current policies, documented responsibilities | □ |
| Risk | Current risk assessment, treatment plans, accepted exceptions | □ |
| Access | Unique IDs, authentication, least privilege, periodic reviews | □ |
| Data | PHI inventory, encryption, lifecycle controls, backups | □ |
| Application | Secure SDLC, testing, vulnerability management, API controls | □ |
| Vendors | BAAs, due diligence, subcontractor oversight, responsibility mapping | □ |
| Incidents | Response plan, breach assessment process, evidence preservation | □ |
| Continuity | Recovery procedures, testing, critical-service dependencies | □ |
| Training | Role-appropriate workforce training and evidence | □ |
| Evidence | Audit trails and documentation retained and accessible | □ |
Documentation and Addressing Compliance Gaps
Every safeguard above only counts during a HIPAA compliance audit if it is documented. OCR investigators look for evidence, not intentions.
- Maintain records of every risk assessment, its findings, and the remediation steps taken.
- Keep workforce training logs showing who was trained, on what, and when.
- Log every identified gap or violation along with the corrective action plan and its completion date.
- Store signed BAAs centrally and review them whenever a vendor’s access scope changes.
When a gap surfaces, whether through an internal review or an incident, document the finding, the fix, and the timeline. A well-documented corrective action often matters more to OCR than the original gap itself.
HIPAA Penalties for Non-Compliance in 2026
Penalties are tiered by culpability and adjusted for inflation each year. Following the January 2026 adjustment, the current structure is:
| Tier | Culpability | Per-Violation Range |
| 1 | Did not know, and reasonable diligence would not have revealed the violation | $145 to $73,011 |
| 2 | Reasonable cause, not willful neglect | $1,461 to $73,011 |
| 3 | Willful neglect, corrected within 30 days | $14,602 to $73,011 |
| 4 | Willful neglect, not corrected within 30 days | $73,011 and $2,190,294 |
Each tier carries an annual cap above $2.19 million per identical violation category. Beyond fines, healthcare remains the costliest industry for data breach recovery, and reputational damage from a public OCR settlement often outlasts the financial penalty itself.
How Can SparxIT Help Build a HIPAA-Compliant Healthcare App?
Meeting every item on a HIPAA compliance checklist while shipping product roadmaps at enterprise speed is a genuine engineering challenge, not just a policy exercise. SparxIT works with healthcare organizations, digital health startups, and enterprise technology teams for HIPAA-compliant healthcare app development from the architecture stage forward, rather than retrofitting compliance after launch.
- Our architecture and platform selection focus on encryption, field-level access control, and audit logging.
- We secure development practices embedded into the SDLC, including code review and penetration testing before release.
- Our healthcare app developers support vendor and BAA evaluations across your full technology stack, including AI and analytics integrations.
- SparxIT offers audit-ready documentation, from risk assessments to policy libraries, built alongside the software itself.
Organizations that need an outside review of an existing system, or a structured path to compliance for a new build, can engage SparxIT’s HIPAA compliance consulting services to close gaps before they surface in an audit.
Conclusion
HIPAA compliance is not a document that sits in a shared drive. It is a continuous discipline spanning legal accountability, engineering architecture, and workforce behavior.
A thorough HIPAA compliance checklist gives technology leaders a shared reference point across all three, turning a dense regulatory framework into concrete, auditable decisions.
Organizations that treat compliance as an architectural principle, rather than a post-launch fix, consistently spend less, move faster, and face fewer surprises when OCR comes calling.
| Disclaimer: This article is for informational purposes only and does not constitute legal advice. HIPAA requirements may vary and change over time. Consult a qualified legal or compliance professional for guidance specific to your situation. |
Partner with Experts
Frequently Asked Questions
Does every healthcare app need to be HIPAA compliant?


Not every app. HIPAA applies to apps that create, receive, maintain, or transmit PHI on behalf of a covered entity or business associate. A general wellness app that is used only for personal tracking, with no connection to a covered entity, typically falls outside HIPAA’s scope.
What is the difference between a BAA and HIPAA compliance?
A BAA is a legal contract establishing that a vendor is accountable for protecting PHI. HIPAA compliance is broader. It also requires the technical safeguards (encryption, access controls, audit logs) and administrative safeguards (risk assessment, training, policies) to actually be in place.
Note: A signed BAA without those safeguards does not make a system compliant.
Does using a HIPAA-compliant platform make my app automatically compliant?
No. The platform typically covers technical safeguards, such as encryption and access controls. Your organization still owns the administrative safeguards, including risk analysis, written policies, workforce training, and breach notification procedures. Both layers are required together.
What apps do healthcare teams most commonly build around HIPAA requirements?
Common systems include patient intake forms, patient portals, referral-tracking workflows, care-coordination dashboards, and scheduling tools. Each involves PHI moving between roles or parties, so access control and audit logging matter across all of them.
How can I make a healthcare app HIPAA compliant?
Start with infrastructure that provides encryption at rest and in transit, field-level role-based access control, tamper-resistant audit logs, and a signed BAA. Then add organizational requirements such as a documented risk assessment, written policies, and workforce training.
What data does HIPAA protect in healthcare apps?
HIPAA protects Protected Health Information (PHI) and its electronic form, ePHI: any individually identifiable health information, including names, dates of birth, diagnoses, treatment records, and billing details, in any format the app stores or transmits.
Can AWS, Azure, or Google Cloud be used to build HIPAA-compliant healthcare apps?
Yes. All three major cloud providers offer BAA and HIPAA-eligible services, but eligibility is not automatic across every product in their catalogs. Teams need to confirm which specific services are covered under the BAA and configure encryption, logging, and access controls correctly.
Note: The cloud provider secures the infrastructure; your team is still responsible for configuring it correctly.